Bugle Blast — News that hits hard

Bugle Blast

Blog

  • MIT BUILDS AN AI BARCODE FOR ZOMBIE CELLS! | Raman + gene maps flag aging “senescent” cells in mice — human tissue next

    MIT BUILDS AN AI BARCODE FOR ZOMBIE CELLS! | Raman + gene maps flag aging “senescent” cells in mice — human tissue next

    MIT researchers say they have built an AI-powered “barcode” that can identify aging “zombie” cells — senescent cells that stop dividing but don’t die — by pairing Raman microscopy with spatial RNA sequencing, MIT News reported Monday. The paper appears in Nature Aging.

    Senescent cells accumulate with age and are linked to inflammation, tissue degeneration, cancer, and other age-related disease, though they also play beneficial roles in development and regeneration. Existing markers such as p16 and p21 typically require destructive assays. Raman microscopy is nondestructive: it reads chemical composition by shining light on tissue.

    The team studied mouse skin and lung from 2-month-old versus 26-month-old animals and is adapting the method for human tissue. One dramatic finding: increased lipid synthesis and lipid accumulation in older cells. Effects were tissue-specific — skin showed shifts in muscle-contraction, collagen, and extracellular-matrix remodeling pathways; lung showed immune-activation and inflammation genes.

    Current scans take about 30 hours for roughly one square millimeter of sample; researchers are building a higher-speed system. Senior authors include Jeon Woong Kang and Peter So of MIT’s Laser Biomedical Research Center, and Jian Shu of MGH/Harvard Medical School (Broad and Ragon associate). Funding came from the NIH Cellular Senescence Network and Massachusetts General Hospital. Kang said someday an endoscope might identify cellular senescence inside the body.

    Sources: MIT News
  • LAWSUIT: AI LABS ILLEGALLY AGREED TO SLOW DOWN! | Anthropic, OpenAI, SpaceXAI, Google hit with class action over Sept. 12 “pace the frontier” chorus

    LAWSUIT: AI LABS ILLEGALLY AGREED TO SLOW DOWN! | Anthropic, OpenAI, SpaceXAI, Google hit with class action over Sept. 12 “pace the frontier” chorus

    A new class-action lawsuit claims Anthropic, OpenAI, SpaceXAI, and Google made an illegal agreement to slow the pace of frontier AI development — and that the coordination cuts the value consumers get from paid AI subscriptions, AP reported via The Hindu.

    The suit, filed Friday in the U.S. District Court for the Northern District of California, centers on Sept. 12, when Anthropic CEO Dario Amodei published an essay urging industry cooperation on decelerating for safety. The same day, OpenAI CEO Sam Altman, SpaceXAI CEO Elon Musk, and Google DeepMind co-founder Demis Hassabis publicly agreed with the thrust of Amodei’s pitch.

    Four named plaintiffs who pay for ChatGPT, Claude, Grok, or Gemini are seeking to represent a nationwide class of paid subscribers. Lead attorney Nick Rowley said: “AI will quickly spin out of human control and could kill us all if we allow AI safety and protocol … to be controlled by private self-serving agreements between the world’s most powerful for profit technology companies.”

    Amodei had acknowledged antitrust concerns and asked for a narrow government waiver for certain safety talks. Altman said OpenAI welcomes a federal safety framework but does not believe the labs need an antitrust exemption to begin. The labs did not immediately respond Saturday. President Trump rejected regulation calls and announced an AI task force plus an “AI czar” Saturday with scant detail. Sen. Josh Hawley has opposed giving the labs an antitrust exemption.

    Sources: The Hindu (AP)

  • HOUTHIS PUSH YEMEN HIGHLANDS AS TRUMP SCRAPS STRIKES! | NYT says bombs were loading when he called it off — Red Sea choke tightens

    HOUTHIS PUSH YEMEN HIGHLANDS AS TRUMP SCRAPS STRIKES! | NYT says bombs were loading when he called it off — Red Sea choke tightens

    Houthi fighters were pushing Monday to seize the Kahboub Mountains heights in Yemen’s Taiz and Lahij provinces — a move aimed at cutting the Red Sea coast off from remaining Saudi-backed areas in the south, Reuters reported.

    The New York Times said the Trump administration prepared Sunday airstrikes after fresh pleas from Saudi Crown Prince Mohammed bin Salman, then called them off at the last minute even as troops were loading bombs onto aircraft. Reuters could not independently verify the report; U.S. Central Command did not respond to a request for comment.

    The Houthis said Saturday they had fired on Riyadh, where loud booms were followed by smoke near the airport. Saudi Arabia has not commented on the first apparent strikes on the capital since the escalation began. The Iran-backed group seized Yemen’s Red Sea coast this month; fighting has centered on Al-Wazi’iyah in Taiz and Ras al-Ara, with Bab al-Mandab control threatening Saudi Arabia’s alternate oil-export route around Hormuz disruption.

    The United Nations says nearly 700 people have been killed and thousands injured in the flare-up, with more than 120,000 Yemenis displaced inside the country and thousands more fleeing by boat to Africa. Satellite data shows Saudi Hormuz exports climbing to about 2.9 million barrels per day recently from just 700,000 in August. U.S. retail diesel hit another all-time high Monday above $6.51 a gallon.

    Sources: Reuters

  • YOUR WORK MFA CAN STILL GET PROXIED! | BigBear PhaaS bypassed Microsoft 365 MFA at 258 orgs — lookalike pages steal the session

    YOUR WORK MFA CAN STILL GET PROXIED! | BigBear PhaaS bypassed Microsoft 365 MFA at 258 orgs — lookalike pages steal the session

    If your day job runs on Microsoft 365, “I got the MFA prompt, so I’m safe” is not enough. BleepingComputer reported Sept. 7 that the BigBear 2.0 phishing-as-a-service (PhaaS) kit — built on Evilginx2 adversary-in-the-middle proxying — completed MFA bypasses at 258 organizations.

    CloudSEK researchers who reached the control panel said the operation exfiltrated 5,137 credential records, including 474 complete MFA-bypassed authentications, 1,032 plaintext passwords, and 4,148 session cookies across 40+ countries. Custom JavaScript interferes with FIDO2/WebAuthn to nudge victims toward weaker methods. Residential proxies matched to ~69 countries help the fake login look local to Microsoft’s checks.

    Frame it for normals: If you type your work email and password into a lookalike Microsoft page, the proxy can capture the session after you finish MFA — and then ride your cookie into Outlook, Teams, and OneDrive. Prefer phishing-resistant passkeys/FIDO2 hardware where IT allows it. If you suspect you phished yourself, tell IT immediately, revoke sessions / sign out everywhere, and reset the password from a known-good device.

    Sources: BleepingComputer (CloudSEK)

  • PASSKEYS AREN’T MAGIC FOR NORMALS! | 39 documented attack paths hit sync, prompts, and recovery — FIDO2 crypto still mostly intact

    PASSKEYS AREN’T MAGIC FOR NORMALS! | 39 documented attack paths hit sync, prompts, and recovery — FIDO2 crypto still mostly intact

    Passkeys are still a big upgrade over passwords — but they are not an invincible force field for regular people. BleepingComputer reported Sept. 4 that researchers have catalogued at least 39 publicly documented attack paths around passkey authentication and the software that surrounds it.

    The important split for normals: the FIDO2 cryptography itself is usually still solid. Attackers go after sync, enrollment, recovery, OS/browser UI prompts, and malware already on your device. SpecterOps’ “Pass-the-Passkey” work showed a malicious Windows app can trigger a legitimate-looking WebAuthn prompt, get you to approve it, and walk away with a signed assertion — private key never extracted, account still compromised. Synced vault passkeys (for example via Google Password Manager on Windows) inherit the weaknesses of the phone, cloud account, and password manager that move them around.

    Practical takeaways: Prefer a hardware security key for email, banking, and your password manager when you can. Keep your OS and browser updated. Treat unexpected passkey pop-ups like unexpected MFA pushes — deny first, then check the real app. Synced passkeys beat reused passwords; they are not “phishing-proof forever.”

    Sources: BleepingComputer; SpecterOps Pass-the-Passkey / Unit 42–style coverage of synced passkey risks on Windows

  • FAKE T-MOBILE “REWARDS EXPIRING” TEXTS ARE A SCAM! | ~18,400 points, urgent deadline, 1,000+ templates — don’t tap the SMS link

    FAKE T-MOBILE “REWARDS EXPIRING” TEXTS ARE A SCAM! | ~18,400 points, urgent deadline, 1,000+ templates — don’t tap the SMS link

    Those “your T-Mobile Rewards points are about to expire” texts are a phishing scam — not a real account notice — Malwarebytes threat intel reported Sept. 17. The campaign has been running since early May 2026, waving invented balances (often ~18,400 points), urgent expiry dates, and links that push you to “redeem” before you can check.

    Researchers found more than 1,000 closely related SMS templates. The story stays the same; only the greeting, headline, point total, and deadline change. Links rotate through lookalike domains patterned like t-mobile.*.top (at least 81 domains over four months) that harvest logins, payment details, and one-time passcodes. Do not type credentials or OTPs after following an unsolicited text link.

    What normals should do: Don’t tap SMS links. Open the official T-Mobile app or type the real site yourself and check Rewards there. Forward suspicious texts to 7726 (SPAM). If you already entered info on a lookalike page, change your password from a trusted device, watch bank/carrier alerts, and treat any “verification code” requests as hostile.

    Sources: Malwarebytes

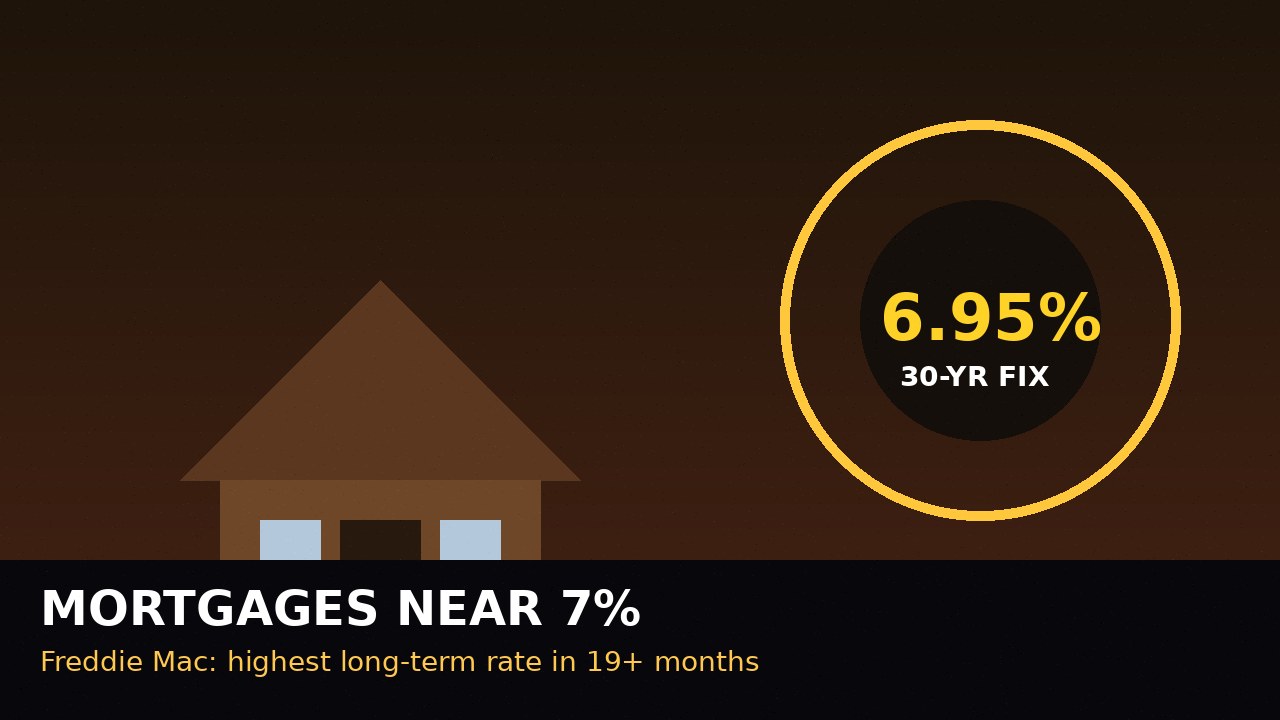
  • 30-YEAR MORTGAGES JUMP TO 6.95% — NEARLY 7%! | Freddie Mac’s long-term rate hits a 19-month high as the Fed’s hike locks in the squeeze

    30-YEAR MORTGAGES JUMP TO 6.95% — NEARLY 7%! | Freddie Mac’s long-term rate hits a 19-month high as the Fed’s hike locks in the squeeze

    The average U.S. 30-year fixed mortgage rate rose to 6.95% for the week ending Sept. 17 — up from 6.76% the prior week and the highest level in more than 19 months — Freddie Mac said Thursday, the Associated Press reported via the New York Post. A year earlier the average was 6.26%. The 15-year fixed average climbed to 6.26% from 6.09%.

    Mortgage rates generally track the 10-year Treasury yield, which breached 5% earlier in the week for the first time since 2023 after inflation and oil-shock fears. The Fed’s Wednesday quarter-point hike to 3.75%–4.00% does not set mortgage rates directly, but bond investors watch Fed policy closely; the central bank also signaled another hike later this year.

    “The rate hike all but guarantees that mortgage rates will remain stuck at or above the 7% threshold,” Bright MLS chief economist Lisa Sturtevant told AP — a psychological and financial barrier that squeezes affordability. Existing-home sales have been stuck near multi-decade lows as higher borrowing costs and thin inventory keep would-be buyers on the sidelines.

    Sources: New York Post (AP); National Association of Realtors

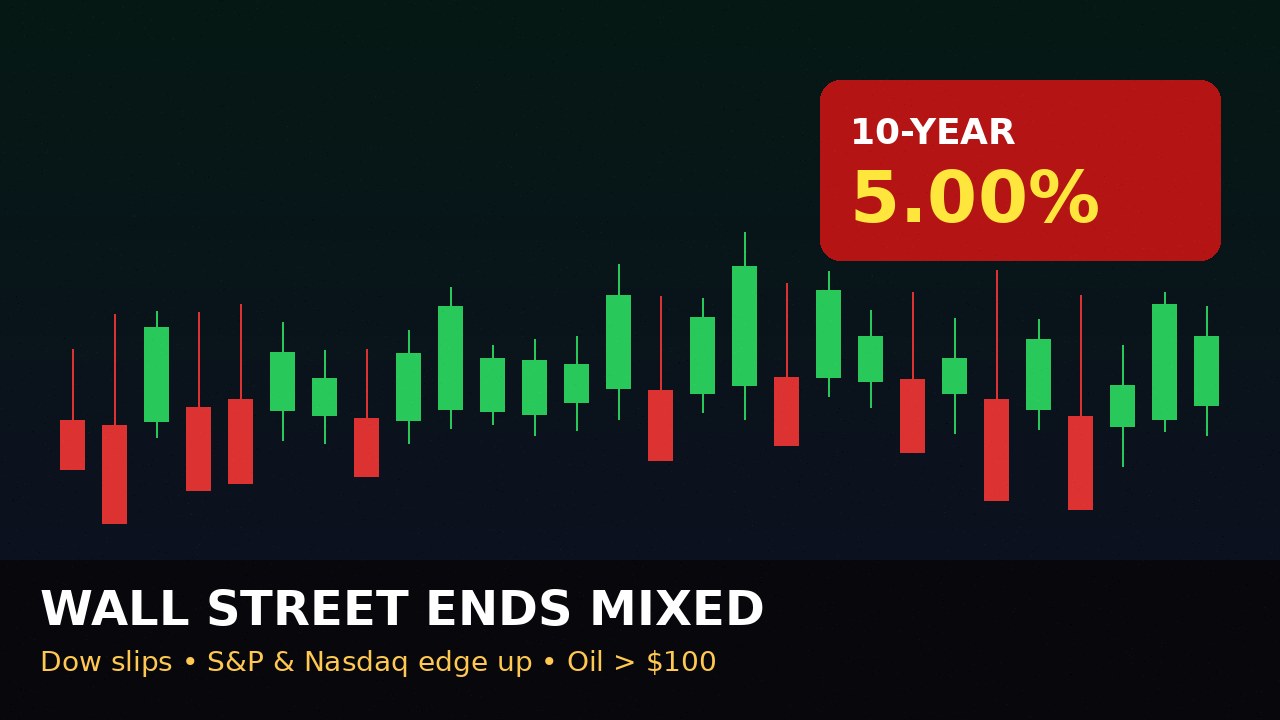
  • WALL STREET ENDS MIXED AS THE 10-YEAR HITS 5%! | Dow slips, S&P and Nasdaq edge up, oil stays above $100 after the Fed’s first hike in three years

    WALL STREET ENDS MIXED AS THE 10-YEAR HITS 5%! | Dow slips, S&P and Nasdaq edge up, oil stays above $100 after the Fed’s first hike in three years

    U.S. stocks closed mixed on Friday, Sept. 18, capping a volatile post-Fed week: the Dow Jones Industrial Average fell 95.40 points (0.18%) to 51,682.64, while the S&P 500 rose 12.74 points (0.17%) to 7,650.50 and the Nasdaq Composite gained 104.25 points (0.40%) to 26,522.55, according to Reuters via The Straits Times and Associated Press figures.

    The 10-year Treasury yield topped 5% during the week — its highest level since 2023 — and oil remained above $100 a barrel, keeping inflation worries front and center even as crude eased from session highs after China, at Saudi Arabia’s request, asked Iran to limit Houthi attacks on Saudi oil infrastructure, The Straits Times reported.

    For the week, the Dow posted its biggest weekly percentage decline since March (about −1.7%), the S&P finished roughly flat to slightly lower, and the Nasdaq ended higher than the prior Friday. CME FedWatch showed about a 55.4% chance of another Fed hike at the October meeting, up from 42.5% a week earlier. Declining issues outnumbered advancers on both the NYSE and Nasdaq as volume ran hot on quadruple-witching expiration day.

    Sources: The Straits Times (Reuters); The Seattle Times (AP)

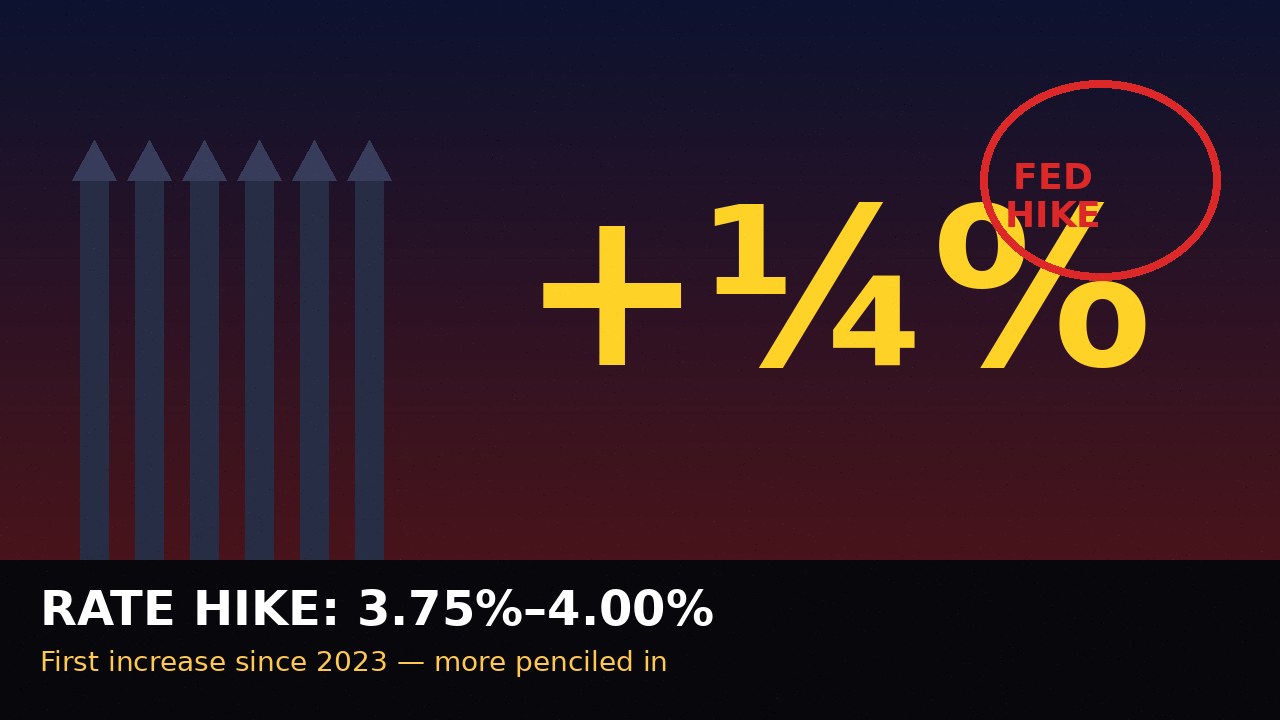
  • FED HIKES RATES FOR THE FIRST TIME SINCE 2023! | Warsh joins a unanimous quarter-point move to 3.75%–4% and pencils in more tightening

    FED HIKES RATES FOR THE FIRST TIME SINCE 2023! | Warsh joins a unanimous quarter-point move to 3.75%–4% and pencils in more tightening

    The Federal Reserve raised its benchmark overnight rate by a quarter percentage point to a 3.75%–4.00% target range on Wednesday — the first hike since 2023 and the first policy shift under Chair Kevin Warsh — in a unanimous FOMC decision aimed at a “timelier” return of inflation to 2%, Reuters reported.

    Updated projections showed 16 of 18 policymakers anticipating at least one more quarter-point increase by year-end, with the median path putting the policy rate in the 4.00%–4.25% range at the end of 2026 and holding there through 2027. Officials marked up PCE inflation to 3.7% for 2026 and do not project a return to the 2% target until 2029. Median real GDP was marked to 2.3% this year, with unemployment ending near 4.1%.

    Warsh told reporters inflation “remains elevated” and said he would be “hard-pressed to describe broad financial conditions as restrictive,” framing the move as removing “a dose of accommodation.” President Trump repeated calls for rates near 1% on Truth Social after the decision; Warsh emphasized the committee’s inflation mandate. CME FedWatch showed markets pricing a high probability of another hike before year-end, Reuters said.

    Sources: Reuters; Federal Reserve (Warsh opening statement); Bloomberg

  • GOLDEN RETRIEVER OFFERS TOYS TO THE BURGLAR! | Nash fails guard-dog school while San Diego owners watch the break-in from 30,000 feet

    GOLDEN RETRIEVER OFFERS TOYS TO THE BURGLAR! | Nash fails guard-dog school while San Diego owners watch the break-in from 30,000 feet

    A San Diego couple watched from an airplane as a burglar climbed into their Sherman Heights home — and their 4-year-old golden retriever, Nash, repeatedly brought the intruder toys to play with, City News Service reported via KESQ and Patch, citing NBC 7 San Diego and the Los Angeles Times.

    Dante Rowley and his fiancée Stephanie Calderon opened their Ring app as their flight took off and saw a ladder propped against a slightly open second-story window. The suspect, John Cline, 57, climbed inside, removed his shirt and shoes, ate yogurt, turkey, and cheese from the fridge, and took a nap — while Nash kept offering different toys. “Nash is not the greatest guard dog,” Rowley told NBC 7. “We thought that he was going to be barking at people, and he did the exact opposite.”

    From the plane, Rowley texted San Diego police and granted live camera access. Officers arrived within minutes, used a drone inside, and arrested Cline on suspicion of first-degree burglary. Nash greeted the cops with a toy, too. Rowley told the Los Angeles Times nothing was stolen and the home was largely undamaged beyond some fridge food and a broken outdoor flowerpot during the escape attempt.

    Sources: KESQ (City News Service); San Diego Patch; NBC News